Showing posts with label national security. Show all posts

Monday, August 17, 2026

Department of War Orders Research Security Audits at 30 Academic Institutions

The Department of War has issued formal notifications to 30 domestic academic institutions, directing them to initiate immediate and comprehensive reviews of their academic, financial and research collaborations with foreign entities of concern.

These notifications address active institutional ties and collaborations with foreign entities identified under Section 1286 of the FY19 NDAA, as well as organizations associated with rebranded Confucius Institutes. Executed by the Office of the Under Secretary of War for Research and Engineering, this action is designed to protect American taxpayer-funded research investments from unauthorized technology transfer, intellectual property theft and adversarial exploitation.

"The Department of War has zero tolerance for academic partnerships that compromise our national security," said Emil Michael, Under Secretary of War for Research and Engineering. "Institutions that receive funding from American taxpayers must uphold the highest standards of research security, and these mandated audits will ensure accountability across the board."

To maintain eligibility for future federal research funding, the notified universities must complete a comprehensive audit of all identified foreign collaborations, assess the exposure of sensitive or export-controlled research, and implement strict mitigation plans, including the termination of problematic partnerships. Institutions are required to report their findings and actions directly to the Department no later than August 31, 2026.

"Universities are critical partners in executing a wide range of Department of War research programs, and the Department must therefore ensure that our research investments are well protected from foreign exploitation," said Dr. Joseph Jewell, Assistant Secretary of War for Science and Technology.

Through these audits, the Department of War will better anticipate emerging threats, adapt to evolving adversarial tactics and maintain America's position as a global leader in innovation. The Department is pursuing this effort alongside partners in Congress. Together with the House and Senate Armed Services Committees, the House and Senate Appropriations Committees and the House Select Committee on the Chinese Communist Party, the Department continues to build a robust research ecosystem that protects critical discoveries from exploitation.

Friday, July 31, 2026

Hegseth: Department Success Buoyed by Courage, Spirit, Leadership

The War Department has had a lot of success in the past 19 months, said Secretary of War Pete Hegseth. And that's in no small part due to the dedication and training of the men and women in uniform who form the heart of the U.S. military.

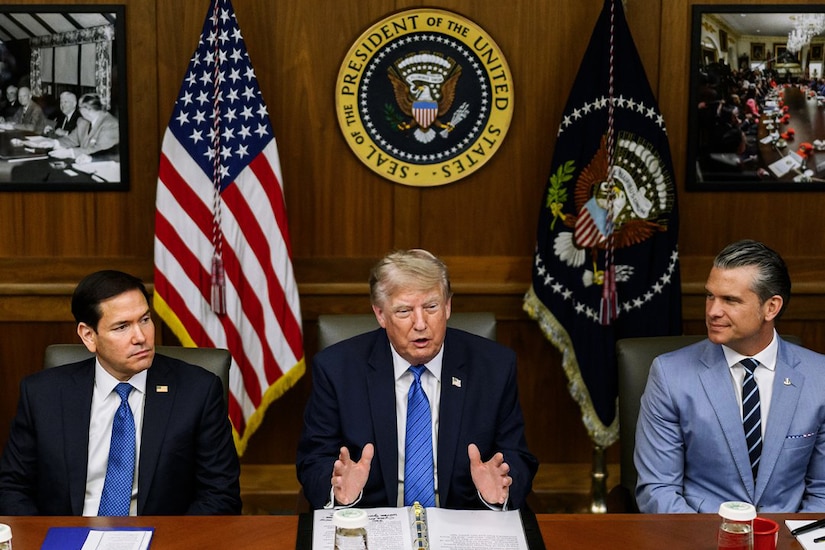
But underwriting that success is presidential leadership from the very top, Hegseth told President Donald J. Trump today during a cabinet meeting at Camp David in Maryland.

Three men in business attire sit next to each other at a table; behind them are an American flag and another flag.

"It's great Americans here and all around the country, and all around the world, who are the core of what keeps us safe," Hegseth said. "But in order to do that, you have to have a leader that's willing to put them in a position to do it."

The secretary listed three things Trump provides that make success possible for American warfighters: courage, a mandate to restore the warrior spirit and a generational investment in making the U.S. military the best it can be.

"I think people miss ... the courage it takes to seal the border, to say we're going to do it, and we're going to do it every single day, and we're going to do it on behalf of the American people," Hegseth said.

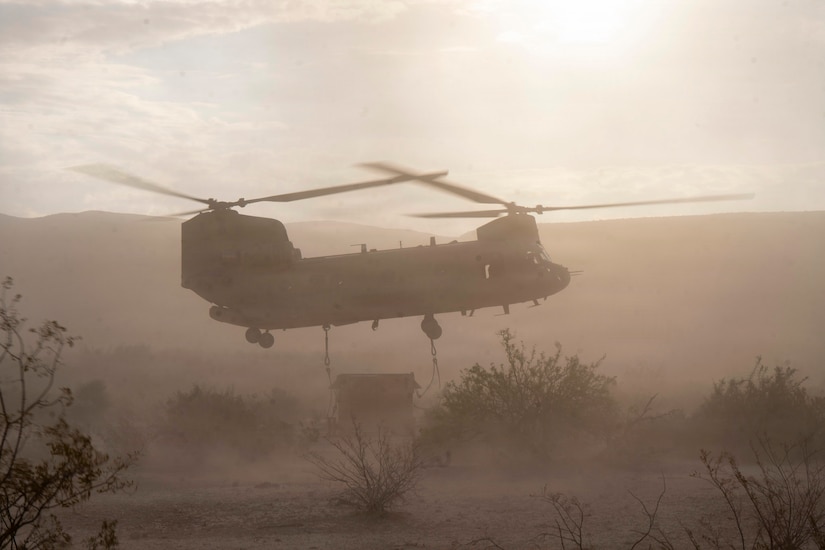
A large helicopter with a sling hanging from it hovers over a square piece of equipment in the dusty desert.

Since January 2025, American troops from all services, and with various skills, have been working first to gain and then maintain 100% operational control of America's southern border and to stop both drug traffickers and the flow of illegal immigration.

"[It takes] courage to bomb the Houthis and say we will maintain freedom of navigation," Hegseth said. "If you wonder why they're not involved in this conflict [in Iran], even though they're a proxy of Iran, it's because they've felt the weight of American power for 45 days, and you had the courage to do that."

In the Red Sea, Iran-backed Houthi forces had been attacking U.S. ships and those of other nations for years, disrupting legal commerce for all. In March 2025, the U.S. took steps to put an end to those attacks during Operation Rough Rider, when U.S. Central Command, at the direction of the president, began a series of attacks at key terrorist Houthi targets in Yemen. Two months later, the president announced that the Houthis agreed to a ceasefire.

Operation Midnight Hammer, the June 2025 mission to obliterate Iran's nuclear capability, also resulted in a ceasefire of the 12-day war, Hegseth noted, calling it a bold move no other president had dared to do.

"Other presidents had the option on their table to do [that], but they never pulled the trigger because of the complications, because of the challenges, because of the risk," he said. "Courage."

The secretary also cited presidential leadership and a willingness to take risks as key enablers for stopping the flow of illegal drugs in the Caribbean, the capture of Venezuelan leader Nicolás Maduro as part of Operation Absolute Resolve and the willingness to undertake the significant Operation Epic Fury, to ensure the Iranian regime will never have a nuclear weapon.

Embolden Spirit

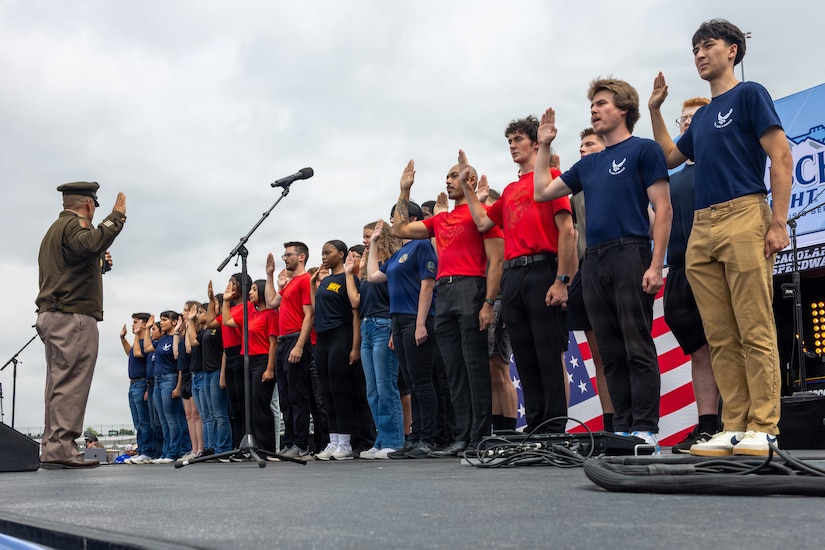
More than a dozen young people stand together on a stage and raise their right hands as a man in a formal military uniform stands in front of them with his own hand raised.

The secretary also credited the president with reinvigorating the spirit of the U.S. armed forces by providing a mandate to eliminate distractions in the force and refocus the warfighter on lethality, meritocracy, accountability, readiness and standards.

"You talk about spirit all the time, and you're right to do so," Hegseth told Trump. "When you rip out [diversity, equity and inclusion], when you rip out social engineering and social justice, and you put in merit; and then you untie the hands of commanders to be commanders, to enforce discipline and accountability, to get back to basics, then you get historic reenlistment inside our ranks."

The secretary said that reinvigorated spirit has caught on across the nation and ignited an interest in serving, adding that the U.S. military is reaping the benefits through increased enlistments and retention.

"Our best people ... are staying, because they want to be in that kind of department," he said. "And then [there is] the historic recruitment record amongst young Americans. Every month our department breaks records."

Investing in Now, Future

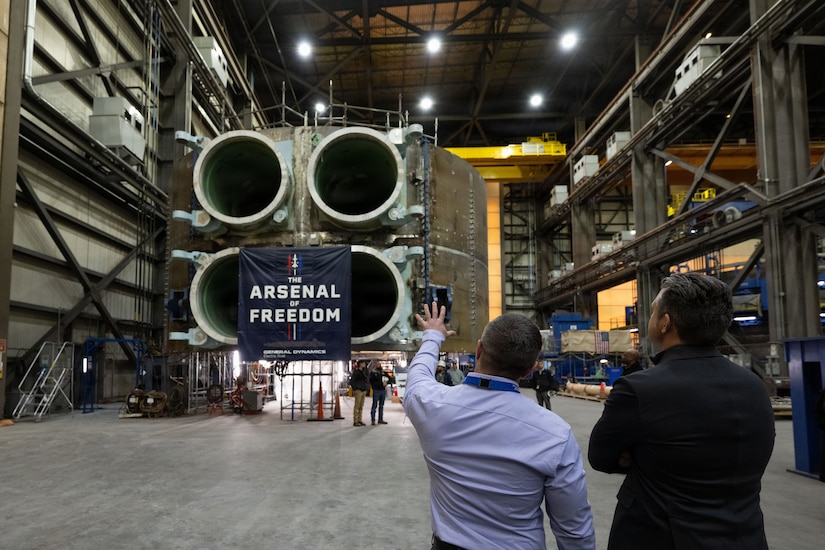
Two men stand near each other and look at a large piece of military hardware inside a large building. A sign hangs off the equipment that says, "The Arsenal of Freedom."

This year, the president has asked for $1.5 trillion to fund the U.S. military. However, Hegseth said it's not going to be business as usual for how that money will be spent, noting that Deputy Secretary of War Steve Feinberg will be responsible for ensuring the money is spent in a way that truly strengthens the department.

"This is a businessman in charge; this is the deputy secretary of our department, who's a turnaround guy, just like the president is — saying we will not fund ... the department the way we have in the past," Hegseth said.

In addition to funding, the secretary highlighted recent efforts to strengthen the defense industrial base, including being a better customer, which has resulted in America's industry partners reinvesting in themselves, ultimately driving down costs to the department.

"[There is] $75 billion in private investment from defense companies that are now investing in new plants, new equipment and new assembly lines, to build the munitions of the future faster than ever possible," the secretary told the president. "That's saving taxpayer dollars because the companies themselves are investing — the arsenal of freedom would never happen without you."

Sunday, October 26, 2025

The Front Lines of Hunger: How the Government Shutdown Starves America’s Military Families

I. Introduction – The New Battlefront

At a base commissary on a quiet weekday morning, a fictional Marine named Staff Sergeant Evans stands in line, uniform pressed, rucksack at his feet. Beside him waits Ms. Jenner, a composite character modeled after furloughed DoD maintenance workers, clutching a grocery list she may not be able to afford to fill. Though these figures are fictional, their circumstances represent the very real struggles unfolding across military installations during the 2025 government shutdown. While active-duty personnel have temporarily received pay through redirected Department of Defense funds, tens of thousands of DoD civilians and contractors have gone weeks without income. The consequences ripple outward — from the barracks to the breakroom to the dinner table — threatening not just mission readiness, but the basic well-being of America’s defenders and those who support them. This essay argues that the shutdown has exposed an invisible front line, where hunger unites soldiers, civilians, and contractors in a shared battle for stability.


II. Background – How a Political Stalemate Became a Human Crisis

When the federal government funding lapsed as of September 30, 2025, agencies entered contingency operations. The Pentagon announced that it would redirect unused research and development funds to ensure mid-October pay for active-duty troops. (Air & Space Forces Magazine) Meanwhile, legislation such as the proposed “Pay Our Military Act” remains stalled. (Federal News Network) The shutdown marks a convergence of high cost-of-living, inflation, frequent relocations, and the low pay of junior enlisted personnel—conditions that already placed some military families in precarious financial positions prior to the lapse.


III. A Fragile Ecosystem: Military Families Already on the Edge

Data from the RAND Corporation show that approximately 25 – 26 % of active-duty service members, and their families, report some level of food insecurity. (RAND) Enlisted families are disproportionately affected, with one study finding 27 % of enlisted active-duty family respondents reporting low or very low food security, compared with just 4 % of officer families. (Blue Star Families) Contributing factors include spouse under-employment (especially after relocations), frequent moves, housing and childcare costs, and a stipend structure (such as Basic Allowance for Housing) that may reduce eligibility for food-assistance programs. (Feeding America Action) These structural pressures mean that even before the shutdown, the defense community was fighting an uphill battle against hunger.


IV. Civilian and Contractor Fallout – The Hidden Threads in Military Life

The military family experience extends beyond the uniformed service member. DoD civilian employees and contractor personnel are part of the base ecosystem — from maintenance, commissary staffing, food service, base housing, childcare, to logistics. During the shutdown, many civilian DoD staffers have been furloughed or required to work without pay; many contracts are paused or delayed due to lack of funding. (AP News) When base support functions falter, the impact falls to families: food-service workers may stop receiving pay, leading to reduced commissary hours; contractors who service base housing may delay repairs, increasing cost burdens on military families; and local economies domiciled around bases — home to many military spouses and contractor households — experience strain. In military communities, one spouse may serve in uniform, another in the civilian or contractor workforce; when one or both paychecks falter, the household’s food security immediately teeters. As a nonprofit executive observed: demand at a military-community food pantry spiked 300 % during the shutdown. (TIME)


V. Commissaries and Food Banks – When Support Systems Collapse

On many bases, the commissary and exchange remain open, but their staffing and operations depend on funding flows and civilian/contractor labor. During the shutdown, reduced hours or temporary closures are reported. (MOAA) Local food-assistance programs tied to military communities are overwhelmed. For instance, the Armed Services YMCA and other organizations report dramatic increases in need among service-members and military-family households. (TIME) At Camp Pendleton and Los Angeles AFB the labels of “military family” now include civilian and contractor families equally reliant on assistance. One base chaplain adds, “We all wear different badges, but we’re all hungry the same.” The convergence of uniformed, civilian, and contractor homelessness or hunger underscores that base communities function as integrated ecosystems.


VI. The Broader Impact – Readiness, Morale, and Trust

Hunger in a household undermines more than nutrition — it affects mental health, morale and military readiness. Studies show that food insecurity in soldiers is associated with increased odds of depression, hazardous drinking, and intent to leave service. (PMC) For service members whose spouse or partner is furloughed or unemployed due to shutdown-induced contractor disruptions, the stress compounds. The pledge “we support our troops” rings hollow when those same troops’ families stand in food-pantry lines. The resulting erosion of trust and morale threatens the very readiness the DoD seeks to uphold. Moreover, local base economies suffer when contractors cut back or furlough employees — reducing the second-tier economic buffer that military families often rely upon.


VII. Policy Solutions – Repairing the Defense Food Chain

Short-Term

  1. Congress should rapidly pass a “Pay Our Military & Defense Workforce Act” guaranteeing pay continuity for active-duty, essential civilian and contractor employees during funding lapses. (National Military Family Association)

  2. The DoD should establish an emergency Defense Food Security Fund—jointly administered with USDA—that can deploy rapid food-assistance grants to military communities facing funding-pause stress.

Structural

  1. Index military pay, Basic Allowance for Housing (BAH), Basic Allowance for Subsistence (BAS) and other allowances to regional cost-of-living and household food-security metrics.

  2. Require quarterly reporting across the defense workforce (uniformed, civilian, contractor) of food-insecurity prevalence and trigger automatic relief when rates exceed thresholds (e.g., 20 %).

  3. Foster public-private partnerships (Rotary, USO, YMCA) to build resilient food-support networks on or near installations, and enlist local businesses servicing the base community.

  4. Reform food-assistance eligibility rules for military families (e.g., exclude BAH from SNAP income calculation) to better align need and support. (Feeding America Action)


VIII. Conclusion – One Team, One Fight

The Marine spouse at the commissary; the civilian technician standing nearby; the contractor’s family in a base-town rental. Three roles, one mission: keeping America’s defenses strong. Yet in the emptiness of a grocery cart, the nation’s promise falters. Hunger inside a military family is not an individual failure—it is a systemic betrayal. The federal government may argue readiness, budget, appropriations—but when those who defend the nation share a food line instead of a mission line, the enemy isn’t hunger—it’s indifference. Until America ensures that no soldier’s child goes hungry, our national security remains incomplete.

How You Can Help

Every community can stand with the men and women who serve. Whether you donate food, volunteer time, or share awareness online, collective action makes an immediate difference. Organizations like Rotary clubs, Armed Services YMCA branches, and civic coalitions are rallying across California and beyond to close the gap left by policy gridlock. You can join this effort by visiting www.feedingmilitaryfamilies.org

 References
Rabbitt, M. P., & Beymer, M. R. (2024). Comparing food insecurity among the U.S. military and civilian adult populations (Report No. ERR-331). U.S. Department of Agriculture, Economic Research Service. (Economic Research Service)
Tong, P. K., Asch, B. J., & Rennane, S. (2023). Military compensation and food insecurity: Analysis in support of the fourteenth quadrennial review of military compensation (Research Report RRA-2923-1). RAND Corporation. (RAND)
“Food insecurity among military families unacceptable, advocates say.” (2024, September 24). Army Times. (Army Times)
“How the government shutdown is affecting troops, families.” (2025, October 1). Military Times. (Military Times)
“Help available for Airmen, Guardians, civilians to mitigate lapse in appropriations impact.” (2025, September 30). U.S. Air Force News. (af.mil)
“Military Hunger.” (2020). Feeding America Action. (Feeding America Action)

Saturday, October 18, 2025

The Quiet War: How 2026 Will Be Fought in Cyberspace, Cryptocurrencies, and Crowds

The next war won’t start with a missile streaking across a black sky. It’s already humming under your fingertips—an electrical storm inside routers and wallets and social feeds. There are no parades, no declarations, no borders to cross. There is only the constant pressure of influence, intrusion, and money in motion. The battlefield is invisible. The soldiers look like us. And the weapons are information, currency, and belief.

America is not sleepwalking into this conflict—we’re scrolling into it. The Quiet War has no single author and no single front. Nation-states stir it. Terror networks exploit it. Criminal gangs profit from it. Lone actors are recruited by it. The rules were never written for it. And 2026 will be the year we either learn to fight in this strange atmosphere or we inhale it until our institutions wheeze.

This essay lays out the operating picture of 2026 through three converging fronts—Cyber, Currency, and Crowds—then connects them to a realistic threat matrix for the United States: domestic violent extremism, transnational jihadist networks (especially ISIS-K), state-enabled proxies, and crime-terror hybrids in the Western Hemisphere. The goal is not to frighten; it is to focus. The Quiet War rewards the disciplined, the integrated, and the fast. Everyone else becomes content.


I. The New Grammar of Conflict

For most of the twentieth century, Western strategy assumed that force is something you can see: formation, mobilization, projection, impact. In 2026 the grammar has been rewritten. Force still matters—but narrative, identity, and liquidity now shape the battlefield long before the first kinetic strike. Call it non-kinetic domain dominance: whoever commands the data flows, the cash flows, and the attention flows wins the shaping fight and narrows the other side’s options.

Three realities define this new grammar:

  1. Speed beats scale. A fragment of code, a synthetic video, a coordinated “influencer” dogpile—each can move faster than policy can react. A day of trending fiction can shatter a year of careful deterrence.

  2. Enablers outrun enforcers. Financial plumbing, shell companies, virtual asset service providers, mixing services, and gray-market remittance channels are adapting faster than compliance regimes. The money that animates extremist plots rarely touches a bank; it passes through a chain of plausible deniability.

  3. The home front is the front. In 2026 the most immediate terrorism danger to Americans is inside the homeland. The same platforms that deliver groceries deliver propaganda, targeting cues, and operational guidance to people who never picture themselves as “combatants” until the moment they act.

A practical conclusion follows: the most dangerous adversaries are not always the ones with the biggest guns—they’re the ones with the best routers, the quietest donors, and the deepest reach into our heads.


II. The Cyber Front: Intrusion as Atmosphere

There is no “peace” in cyberspace. There is only constant contact—probing, mapping, stealing, pre-positioning, and sometimes flipping the switch when the stakes or the message warrants it. What changes in 2026 is not the existence of this contact but its automation and autonomy.

State actors—Russia, China, Iran, North Korea—will continue to drive the highest-end intrusions against critical infrastructure, defense industrial targets, and media platforms. They will also continue to outsource deniable operations to quasi-patriotic hacker groups and cut-outs. But the rising noise floor comes from the commercialization of sophisticated capabilities: AI-assisted spear phishing, large-scale credential stuffing, automatic lateral-movement kits, and marketplaces where zero-days are sold like concert tickets.

Non-state actors are already adapting. Jihadist and extremist communities don’t need to invent new tools; they simply rent them and hide in the traffic. Expect three developments to define 2026:

  • AI-augmented intrusion at scale. Models trained to profile an organization’s social graph and craft individualized phish at machine speed will make yesterday’s “good tradecraft” seem quaint. The goal is not to breach one target; it is to breach thousands, cheaply.

  • Supply-chain subversion for narrative effect. Attacks that swap code libraries, poison updates, or tamper subtley with content pipelines will be designed as psychological operations as much as technical ones. Imagine your trusted software pushing a “security alert” that is actually a rumor.

  • Ransomware with a political payload. Criminal crews will continue to monetize chaos. But watch for a sharper overlap: ransomware timed to civic events, or “leaks” engineered to feed extremist narratives. Profit and politics are not rivals—they are roommates.

Cyber risk will not distribute evenly. Hospitals, regional utilities, municipal systems, and small defense suppliers remain softest because they are essential but thinly resourced. The Quiet War goes where the doors are unlocked and the pain is high.

The old comfort—“they’ll hit the big cities first”—is obsolete. In cyberspace, every town is a capital.


III. The Currency Front: Money in the Shadows

Follow the money and you find the plot, the logistics, the loyalty. You also find the weak points in a global economy built for speed and convenience, not hard attribution.

In 2026, the terrorist-financing picture is a web of old ingenuity and new rails:

  • Traditional methods—hawala, bulk cash, trade-based money laundering—will persist. They’re durable because they fit local cultures of trust and because they hide in legitimate commerce.

  • Virtual assets lower friction. Cryptocurrencies and tokenized stores of value do not create illicit finance; they simply accelerate it, reduce overhead, and offer an illusion of anonymity. “Mixers” and cross-chain bridges complicate tracing. “Stablecoins” reduce volatility risk for illicit treasuries.

  • Front organizations, sham NGOs, and shell companies remain the great equalizers. They convert dirty flows into clean contracts and humanitarian cover, then back again. As one watchdog put it, the shell company is the getaway car of global finance.

What’s new in 2026 is the convergence of automation and opacity. Expect to see:

  • AI-managed laundering that monitors on-chain heuristics and shifts routes dynamically as analysts close in.

  • Exploiting humanitarian and conflict flows—using real crises and real charities as camouflage to move money to fighters who destabilize the same communities donors think they’re saving.

  • Micro-financing of terror through thousands of small transactions designed to never trip a threshold or provoke a file. It’s not the one big wire anymore; it’s the drip-drip that fills the barrel.

Financial intelligence officials already warn that our regulations are chasing a shape-shifting adversary. In a world where a smartphone can become a bank, compliance is a moving target and the bad actors have more time to aim.


IV. The Crowd Front: Weaponized Attention

The old propaganda playbook targeted ideology; the new one targets identity. It isn’t trying to persuade you with argument; it’s trying to trigger you with emotion. That makes everyone susceptible. It’s easy to picture the “other side” as the only target. The truth is colder: anyone who can be enraged can be enlisted.

The engineering of mass behavior in 2026 will lean on four accelerants:

  1. Generative AI as an attention multiplier. Synthetic news anchors, voice-cloned officials, “citizen footage” that never happened—high-quality fakes tuned to your fears. The aim isn’t perfect realism; it’s plausible urgency.

  2. Algorithmic herding. The crowd moves when it believes the crowd is moving. You don’t need millions of bots; you need a few thousand accounts to simulate momentum and your target’s network will do the rest.

  3. Micro-targeted grievance. Adversaries don’t push a single narrative; they plant conflicting narratives calibrated to fracture social trust—law enforcement vs. communities, veterans vs. activists, “patriots” vs. “traitors.” The goal is not to win an argument. It’s to make civil argument impossible.

  4. Street-to-screen feedback loops. Protests and counter-protests become laboratories for content. A single clash edits into a thousand different “truths,” each confirming a separate faction’s suspicions. Extremists fish in these waters for recruits. Terrorists look for cover.

If the meme is the new missile, then friction is the new air defense. Platforms and communities that slow virality, that reward context and penalize incitement, blunt the weapon. But friction and profit rarely coexist. That is the national dilemma we keep postponing.


V. The Threat Picture for 2026

The three fronts converge into a threat matrix. Not every actor uses every tool; not every danger is equal. But the pathways are consistent.

1) Domestic Violent Extremism (DVE)

The most persistent and immediate risk to Americans remains homegrown—small cells and lone actors radicalized through grievance content, guided by accessible tradecraft, and financed at trivial cost. The ideology is not a single flag; it is a marketplace of rage: racially or ethnically motivated extremism, violent anti-government currents, accelerationist fantasies, and retaliatory violence around domestic flashpoints. The signature of 2026 is less the spectacular plot and more the sustained pressure of low-complexity attacks against soft targets.

Cyber and currency amplify this. A radicalized individual can acquire instruction, reconnaissance, and money without leaving a digital footprint that looks any different from normal life: a shopping list of dark-market items, a cascade of “tutorials,” a handful of anonymous donations, and a narrative that promises immortality in fifteen seconds of infamy.

Expect targeted violence against civic spaces, faith communities, government facilities, law enforcement, and symbolic cultural venues. The psychological objective is to convince Americans that we cannot live together, cannot debate without blood, cannot trust the person in the next line. If the Quiet War breaks the American imagination, kinetic attack becomes merely punctuation.

2) ISIS-K and the Post-Caliphate Network

The Islamic State lost its caliphate but not its method. Its brand survives as a franchise model across Africa and Central Asia, and its most dangerous offshoot for external plotting remains ISIS-K. It is both a local player in Afghan-Pakistani dynamics and a global impresario of inspiration: it curates grievances, circulates training, claims credit for mayhem it merely fertilized, and occasionally directs or facilitates something bigger.

The 2026 risk is twofold:

  • Inspiration pipelines—online radicalization that translates into attacks with little command-and-control signature in the West.

  • External-operations facilitation—small networks using conflict zones and permissive borders for travel, training, or staged propaganda designed to provoke overreaction.

The network’s financial strain is real; salaries have fallen, recruitment pools fluctuate, and counter-terrorist finance (CTF) scrutiny has improved. But austerity can make terrorism more dangerous, not less, because it drives reliance on cheapest methods: small arms, edged weapons, vehicle rammings, crude IEDs, simple cyber-enabled harassment. These are low-cost, high-terror per dollar.

3) Al-Qaida Affiliates and the Sahel’s Expanding Fire

The center of gravity for jihadist territorial ambition shifted toward Africa, especially the Sahel and East Africa, where security vacuums and governance stresses allow al-Qaida-aligned coalitions and Islamic State affiliates to recruit, tax, and terrorize. This matters to the United States even when it feels geographically distant. American diplomats, contractors, aid workers, and commercial interests operate in these zones. The guarding of ports and corridors that feed global supply chains depends on regional stability. And every ungoverned space invites external-ops incubation.

For 2026, the most realistic U.S. exposure is indirect: kidnap-for-ransom, attacks on partners, and maritime disruptions radiating from coastal penetration by Sahel insurgencies. But indirect does not mean unimportant. Small fires in fragile places can cast global smoke.

4) State-Enabled Proxies and Gray-Zone Tactics

Terrorist tactics are no longer the exclusive property of “terrorist organizations.” States sponsor, shelter, or look away when proxies act in their interest. They wage campaign-length cyber operations below the threshold of open war. They use quasi-legal information outfits to launder narratives into Western discourse. They strike dissidents abroad and call it policing. They mix criminal profit with political intimidation.

This is not the Cold War; it is colder. And it means that some of the most sophisticated adversaries the United States faces in 2026 will be hybrids: part intelligence service, part criminal enterprise, part ideological movement, each piece disposable if exposed. You cannot deter what can always claim it doesn’t exist. You can only raise the cost and shorten the runway.

5) Crime-Terror Hybrids in the Western Hemisphere

Cartels and gangs are not “terrorists” in the strict legal sense, but many have adopted terroristic methods—assassinations, bombings, mass intimidation—to control territory and political outcomes. In parts of Latin America this convergence has produced instability whose shockwaves reach U.S. communities through migration surges, supply chain risk, and diaspora-targeted violence.

The Quiet War cares little about our labels. When a criminal group uses terror tactics, the effect on local populations and regional governance is the same. And when those groups partner with ex-insurgents or foreign enablers for weapons, training, or laundering, the problem becomes strategic.


VI. Likely Scenarios in 2026

Forecasts are not prophecies. But smart preparation begins with plausible arcs:

  1. A lone-actor attack against a civic venue, inspired by domestic or transnational propaganda, executed with low-tech means, broadcast live. The damage is limited; the political aftershock is not.

  2. A coordinated ransomware wave against hospitals or utilities in several states, timed to a polarizing national event. The attackers claim ideology; the wallets end in familiar criminal hands. Crime and cause become mutually reinforcing alibis.

  3. A high-profile disruption traced to a compromised AI or data pipeline, where manipulated information drives a financial panic or a public safety failure. The post-mortem reveals a months-long operation that looked like routine traffic at every step.

  4. A kidnapping or targeted killing of U.S. partners in West Africa, claimed by a jihadist faction, amplified by affiliates for recruitment, and financed through a chain of small donations that never trigger a threshold.

  5. A gray-zone operation against diaspora activists on U.S. soil, blending surveillance, intimidation, and cyber harassment. The sponsor denies involvement; the victims lose faith in protection; the message to others is received.

None of these scenarios require an army. All of them require readiness—technical, legal, and cultural.


VII. How We Win the Quiet War

There is no silver bullet, only a stack: tools, partnerships, habits. The stack must be faster than the threat and harder to break than the story the threat tells.

1) Harden the Domestic Cognitive Space

  • Make community-based prevention boringly normal. It works best when it looks like school programs, public-health models, and faith-community partnerships—when it speaks the language of belonging, not bureaucracy. We will not de-radicalize by lecture. We will pre-radicalize by invitation.

  • Modernize legal friction for virality. The First Amendment’s protection of speech is non-negotiable. But amplification is not speech; it is a product feature. Platforms that profit from algorithmic herding should carry a duty of due care when intelligence flags crisis conditions. The law does not have to define truth to dampen incitement.

  • Train a citizenry that can recognize weaponized content. Media literacy is not a luxury subject. It is digital civil defense. Teach adolescents how to spot synthetic media the way we taught earlier generations how to spot fake checks.

2) Starve the Money

  • Terrorist finance is a plumbing problem. Fix the pipes. Close the loopholes for shell companies, enforce beneficial-ownership transparency, demand real compliance from virtual asset service providers, and audit the humanitarian sector’s susceptibility to exploitation with respect and resolve.

  • Treat mixers and cross-chain bridges like high-risk financial services. Not every privacy tool is a crime tool, but the ones that function like unregistered laundries should face the same scrutiny. If a bridge’s business model depends on opacity, the rest of us are paying the bill.

  • Expand trade-based money-laundering analytics. Terror money is increasingly hidden in shipping paperwork and invoice games. The countermeasure is pattern-matching at scale across customs, banks, and logistics firms, with legal authorities that allow sharing fast.

3) Build Real Cyber Resilience

  • Push security into the bottom of the market. National programs should subsidize basic hardening for hospitals, municipalities, and small suppliers—MFA, patch pipelines, offline backups, tabletop exercises. The cost of not doing this is paid in ambulances and brownouts.

  • Assume breach, practice recovery. The fastest way to defang ransomware is to make it boring for the attacker: immutable backups, segmented networks, and rehearsed playbooks that bring the lights back in hours, not days.

  • Treat information systems like safety systems. When AI and data feeds steer real-world decisions—dispatching, triage, utility loads—apply the rigor we use for aviation: testing, auditing, red-teaming, and mandatory reporting of serious near misses.

4) Think Like a Network, Not a Silo

  • Fuse intelligence without drowning in it. The Quiet War produces oceans of “signals.” The answer isn’t to collect more; it’s to prioritize better and share faster with those who can act—state fusion centers, local partners, and the private sector.

  • Tie foreign and domestic CT in one narrative. The same group that menaces a contractor in West Africa may inspire a teenager in Milwaukee. Our strategies should reflect reality: one network, many faces.

  • Elevate financial intelligence to co-equal status with the kinetic kill chain. If you cut the money—quietly and relentlessly—you cut the muscle memory that makes plotting possible.


VIII. What to Watch (2026 Indicators)

  • A sharp rise in small-value, high-velocity on-chain movements around conflicts and protests—signals of micro-financing or covert redistribution.

  • A mainstream platform caught amplifying a synthetic incident before verification—evidence that our cultural “immune system” is still too slow.

  • Regional coups or collapses in the Sahel that open a corridor to coastal states—test cases for whether jihadist expansion can leverage maritime access.

  • Evidence of state-enabled proxy activity in North America or Europe targeting dissidents or diaspora leaders—gray-zone tactics crossing legal red lines.

  • A major hospital system reduced to pen-and-paper for days due to ransomware—signalling that we continue to under-invest in the bottom tier of critical infrastructure.

When any of these appear, the response must be whole-of-nation and on the clock. In the Quiet War, victory belongs to the side that acts before the narrative hardens.


IX. The Stakes

A skeptic might say: This is melodramatic. America is strong; we’ve seen worse. They’re right about the strength. They’re wrong about the form of the test.

The Quiet War is not trying to defeat our military. It’s trying to exhaust our civic capacity, erode our trust in one another, and make us mistake inconvenience for oppression, rumor for proof, performance for policy. It’s trying to convince us we’re alone. We are not.

What we decide in 2026 is whether we will adapt. Whether we will fight for the spaces between us with the same seriousness we bring to the spaces beyond us. Whether we will invest in the boring things that make bright things possible: backups, audits, local partnerships, shared facts, honest disagreements, slow conclusions.

The missiles may never fly. The invasions may never march. Yet the war is here—inside the signal, inside the wallet, inside the crowd. The question is not whether we will fight. The question is whether, by the time we notice, the fight has already chosen us.


References (no hyperlinks)

  1. U.S. Department of Homeland Security. Homeland Threat Assessment 2025. Washington, DC: DHS, September 30, 2024.

  2. Office of the Director of National Intelligence. Annual Threat Assessment of the U.S. Intelligence Community 2025. Washington, DC: ODNI, March 18, 2025.

  3. Defense Intelligence Agency. Worldwide Threat Assessment: Statement for the Record to the House Armed Services Committee (2025). Washington, DC: DIA, 2025.

  4. U.S. Department of Homeland Security. National Terrorism Advisory System Bulletin, June 22, 2025.

  5. Financial Action Task Force (FATF). Comprehensive Update on Terrorist Financing Risks (2025). Paris: FATF, July 8, 2025.

  6. Financial Crimes Enforcement Network (FinCEN). Advisory FIN-2025-A001: ISIS-Related Illicit Financial Activity. Washington, DC: U.S. Department of the Treasury, April 1, 2025.

  7. Europol. European Union Terrorism Situation and Trend Report (TE-SAT) 2024. The Hague: Europol, December 12, 2024.

  8. Europol. Major Developments and Trends on Terrorism in Europe in 2024 (press summary). The Hague: Europol, June 24, 2025.

  9. United Nations Security Council, Counter-Terrorism Committee/CTED. Briefing on the Secretary-General’s Strategic-Level Report on ISIL/Da’esh, February 7, 2025.

  10. Associated Press. “Islamic State and al-Qaida Threat Is Intense in Africa, with Growing Risks in Syria, UN Experts Say.” AP News, August 2025.

  11. Reuters. “Financial Crime Watchdog Calls for Countries to Come Clean on Shell Companies.” Reuters Business, September 3, 2025.

  12. FATF. “The Financial Action Task Force: Mandate and Areas of Work.” Paris: FATF, 2025.


Author’s Note on Method

This assessment synthesizes publicly available U.S. government threat reporting, European law-enforcement trend data, international counter-terror finance findings, and mainstream wire-service coverage of UN expert reporting and global regulatory updates through October 2025. It prioritizes patterns that are stable across multiple sources (e.g., domestic violent extremism as the leading homeland threat; terrorist-financing adaptability; ISIS-K’s external-ops posture; the Sahel’s expanding insurgent footprint) while recognizing that specific incident risk fluctuates with geopolitical shocks.

Tuesday, August 08, 2023

Two U.S. Navy Servicemembers Arrested for Transmitting Military Information to China

In a striking blow to national security, two U.S. Navy servicemembers have been arrested for their involvement in transmitting sensitive military information to the People’s Republic of China (PRC). The arrests, which took place in the Southern and Central Districts of California, underscore the ongoing threat posed by espionage activities targeting the United States.

Assistant Attorney General Matthew G. Olsen of the Justice Department’s National Security Division expressed the gravity of the situation, stating, “These individuals stand accused of violating the commitments they made to protect the United States and betraying the public trust, to the benefit of the PRC government.” Olsen emphasized that the Department of Justice is fully committed to utilizing all available resources to counter threats from China and deter those who aid in breaking U.S. laws and compromising national security.

Assistant Director Suzanne Turner of the FBI’s Counterintelligence Division echoed Olsen's concerns, highlighting the unrelenting efforts of the People’s Republic of China to undermine American democracy. She noted that the servicemembers' actions had compromised U.S. national security by leaking sensitive military information.

Case 1: United States v. Jinchao Wei

In the Southern District of California, U.S. Navy sailor Jinchao Wei, also known as Patrick Wei, was arrested on espionage charges as he reported for duty at Naval Base San Diego. Wei is accused of conspiring to send national defense information to a Chinese intelligence officer. The indictment alleges that Wei, serving as a machinist’s mate on the U.S.S. Essex, an amphibious assault ship stationed at Naval Base San Diego, provided sensitive national defense information to the Chinese intelligence officer.

The indictment revealed that Wei communicated with the intelligence officer beginning in February 2022. This communication involved sharing photos, videos, and documents related to U.S. Navy ships and their systems. The indictment further outlined how Wei was paid thousands of dollars in exchange for this information. Additionally, he sent technical manuals, including critical technology data, to the intelligence officer. The indictment states that Wei knowingly violated export control regulations by transmitting this information without the required license.

Case 2: United States v. Wenheng Zhao

Petty Officer Wenheng Zhao, also known as Thomas Zhao, was arrested in the Central District of California following an indictment by a federal grand jury. Zhao is accused of receiving bribes in exchange for transmitting sensitive U.S. military information to an individual posing as a maritime economic researcher. The indictment alleges that Zhao, stationed at Naval Base Ventura County, received bribes from a Chinese intelligence officer in return for disclosing non-public sensitive U.S. military information.

Zhao's actions allegedly involved recording and transmitting U.S. military information, photographs, and videos. The information he provided included operational plans for a large-scale U.S. military exercise and electrical diagrams for a radar system in Okinawa, Japan. In exchange for this information, Zhao received payments from the Chinese intelligence officer.

Both cases underscore the urgency of countering espionage and protecting national security. The accused servicemembers face significant penalties if convicted.

The investigations were conducted by the FBI's Counterintelligence and Cyber Division, along with the Naval Criminal Investigative Service (NCIS). IRS Criminal Investigation provided substantial assistance.

Assistant U.S. Attorneys and Trial Attorneys from the Department of Justice's National Security Division are prosecuting the cases.

An indictment is an allegation, and all defendants are presumed innocent until proven guilty in a court of law.

Friday, June 02, 2023

Former U.S. Air Force Officer Sentenced: Unveiling the Breach of National Security Secrets

Former U.S. Air Force Lieutenant Colonel, Robert L. Birchum, was sentenced to three years in federal prison and fined $25,000 by U.S. District Judge Kathryn Kimball Mizelle in Tampa, FL. Birchum pleaded guilty to unlawfully possessing and retaining classified documents related to national defense on February 21, 2023.

During his 29-year career in the Air Force, Birchum held various intelligence positions, working with classified information for prominent agencies such as the Joint Special Operations Command and the Office of the Director of National Intelligence. Despite having entered into agreements to protect classified information, Birchum violated these obligations.

In 2017, law enforcement discovered that Birchum had knowingly taken over 300 classified files and documents, including more than 30 labeled as Top Secret, from authorized locations. He stored these materials in unauthorized places such as his home, overseas officer's quarters, and a storage pod in his driveway. Among the confiscated items were two documents on a thumb drive found at Birchum's residence, containing sensitive information about the National Security Agency's capabilities, collection methods, and vulnerabilities of targets. Both documents were classified as Top Secret/SCI, and their unauthorized release posed a grave threat to national security.

U.S. Attorney Roger Handberg emphasized the serious risk that Birchum's actions posed to national security, thanking law enforcement partners for their commitment to safeguarding the nation. FBI Tampa Special Agent in Charge David Walker highlighted the FBI's dedication to protecting the secrets of the U.S. Intelligence community and ensuring the security of the country.

The case was investigated by the U.S. Air Force Office of Special Investigations and the FBI. Assistant U.S. Attorney Cherie L. Krigsman of the Middle District of Florida, along with Trial Attorney Evan N. Turgeon from the National Security Division's Counterintelligence and Export Control Section, prosecuted the case.

This sentencing serves as a reminder of the government's determination to pursue individuals who knowingly endanger national security and the critical importance of upholding classified information protocols.

Friday, June 22, 2012

Reforms Improve DOD’s Security Clearance Process, Official Says


By Donna Miles
American Forces Press Service

WASHINGTON  – Reforms in the personnel security clearance process have improved the speed and efficiency of background investigations and adjudications with a direct, positive impact on the Defense Department’s ability to carry out its mission, a senior defense official told Congress today.

Streamlined policy and processes have cut duplication and waste, Elizabeth A. McGrath, the Pentagon’s deputy chief management officer, told a subcommittee of the Senate Homeland Security and Governmental Affairs Committee.

Reforms also have reduced the time required to adjudicate clearances even lower than the 20-day goal Congress set in the Intelligence Reform and Terrorism Prevention Act of 2004, to as little as seven days, she reported.

McGrath attributed this success in large part to a new electronic adjudication capability developed by the Army and now deployed across DOD. The Case Adjudication Tracking System enabled the department to adjudicate 110,000 cases – or 24 percent of its secret clearance applications -- electronically last year, she said. This, in turn, freed up adjudicators to concentrate on other, more complex cases.

Other federal agencies have expressed interest in this technology, McGrath told the panel. So far, the Department of Energy has adopted the new system, and the Social Security Administration plans to do the same next year, she said.

In addition, DOD also has initiated a “robust” adjudicator certification program that ensures all adjudicators receive comprehensive, standardized training, McGrath reported.

“The results are clear, she said of the reform initiatives. “We have a higher-quality security clearance program today.”

One of the tangible measures of that progress was the Government Accountability Office’s removal of the DOD personnel security clearance process form its “High-Risk list” last year, she noted. The list, provided to Congress every two years, identifies federal programs at high risk for waste, fraud, abuse mismanagement or in need of broad reform.

DOD’s improved personnel security clearance process has a sweeping impact on the Defense Department, McGrath said. “It improves our ability to safeguard classified material, place qualified individuals in jobs faster, effectively use our contractor workforce, and reduce the burdens and inconveniences on both the federal workforce and our military members,” she reported.

Joining officials from the Government Accountability Office, Office of Management and Budget, Office of Personnel Management and Office of the Director of National intelligence at today’s hearing, McGrath credited the Joint Reform Team founded five years ago with paving the way for these strides.

One of the big outcomes, she said, was the establishment of the Performance Accountability Council that bridges agency divides and keeps each agency on track toward even greater efficiencies.

The work isn’t yet done, McGrath said, emphasizing the importance of continued collaboration in reaching toward greater efficiencies and cost-effectiveness in background investigations and adjudications.

“Our results represent the progress possible when agencies commit to joint goals informed by government-wide priorities and establish proper controls to ensure results,” she said.

Monday, March 26, 2012

Panetta Visits NSA, Cyber Command Leadership


By Army Sgt. 1st Class Tyrone C. Marshall Jr.
American Forces Press Service

WASHINGTON  – Defense Secretary Leon E. Panetta met today with the leader of the National Security Agency and U.S. Cyber Command, said Pentagon Press Secretary George Little.

“Today Secretary Panetta visited the National Security Agency and U.S. Cyber Command at Fort Meade, Maryland, where he met with General Keith Alexander, commander, U.S. Cyber Command, and director, National Security Agency, Central Security Service, and the organizations' leadership,” Little said.

Little said Panetta observed technology demonstrations and received briefings about key issues in the cyber arena.

Panetta’s “discussions focused on efforts to enhance information sharing across the Defense Department and the intelligence community,” Little said.

According to Little, Panetta said he was deeply impressed by team efforts to defend America against cyber attack.

“The secretary acknowledged the critical and important work that the Cyber Command and NSA team are accomplishing, and continues to stress the importance of developing cyber capabilities to meet emerging cyber threats,” Little said.